
India ranks second in ransomware attacks: Report:
The report indicates an alarming 18% increase in global ransomware incidents year-over-year
financialexpress.com/life/technology-india-ranks-second-in-ransomware-attacks-report-3640481/

Story Details
| Last Updated | |
| Total Articles | 4 |
Main Topics


field that develops and studies software enabling machines to exhibit intelligent behavior
News on this topic

dlvr.it Oct 15 24
Microsoft says more ransomware stopped before reaching encryption: Volume of attacks still surging though, according to Digital Defense Report
theregister.com/2024/10/15/microsoft_ransomware_attacks/
dlvr.it Oct 14 24
Would banning ransomware insurance stop the scourge?: White House official makes case for ending extortion reimbursements
theregister.com/2024/10/14/ransomware_insurance_ban/

Similar to This
Previous

CISA: SafePay ransomware hit over 600 critical infrastructure orgs: The Cybersecurity and Infrastructure Security Agency (CISA) says the SafePay ransomware gang ...
bleepingcomputer.com/news/security/cisa-and-fbi-safepay-ransomware-has-hit-over-600-critical-infrastructure-organizations/

Hackers steal children's data after company used 'Password1' for old account: The data watchdog reprimanded Ogi Networks Limited and Data Cymru after the 2024 ...
bbc.co.uk/news/articles/c6r7y03e9m3ro


Hackers used AI in most ransomware attacks and threatened staff, Semperis report found
qz.com/semperis-ransomware-report-ai-attacks-staff-threats-101526


Tech Times Sep 30
AI Ransomware Wiped 100 Azure Accounts in 7 Minutes: Only Pre-Configured Locks Survived
techtimes.com/articles/328096/20260928/ai-ransomware-wiped-100-azure-accounts-7-minutes-only-pre-configured-locks-survived.htm

Ransomware uses AI agents to specifically devastate Azure environments: A ransomware group has begun to specifically devastate Azure environments with AI-powered ...
winfuture.de/news,161607.html

CISA: Windows BlueHammer flaw now exploited by ransomware gangs: CISA confirmed on Monday that ransomware gangs are now exploiting a Microsoft Defender privilege ...
bleepingcomputer.com/news/security/cisa-windows-bluehammer-flaw-now-exploited-by-ransomware-gangs/
dlvr.it May 19
Microsoft disrupts alleged malware-signing operation used by ransomware gangs: 'Thousands' of US victims, including 12+ machines owned and operated by Redmond
theregister.com/security/2026/05/19/microsoft-disrupts-alleged-malware-signing-operation-used-by-ransomware-gangs/5243013
Microsoft disrupts ransomware attacks targeting Teams users: Microsoft has disrupted a wave of Rhysida ransomware attacks in early October by revoking over 200 ...
bleepingcomputer.com/news/microsoft/microsoft-disrupts-ransomware-attacks-targeting-teams-users/

Romania Insider Oct 17 25
Microsoft: Romania ranks 52nd globally in terms of impact of cyberattacks in the first half of 2025
romania-insider.com/microsoft-romania-cyberattacks-first-half-2025
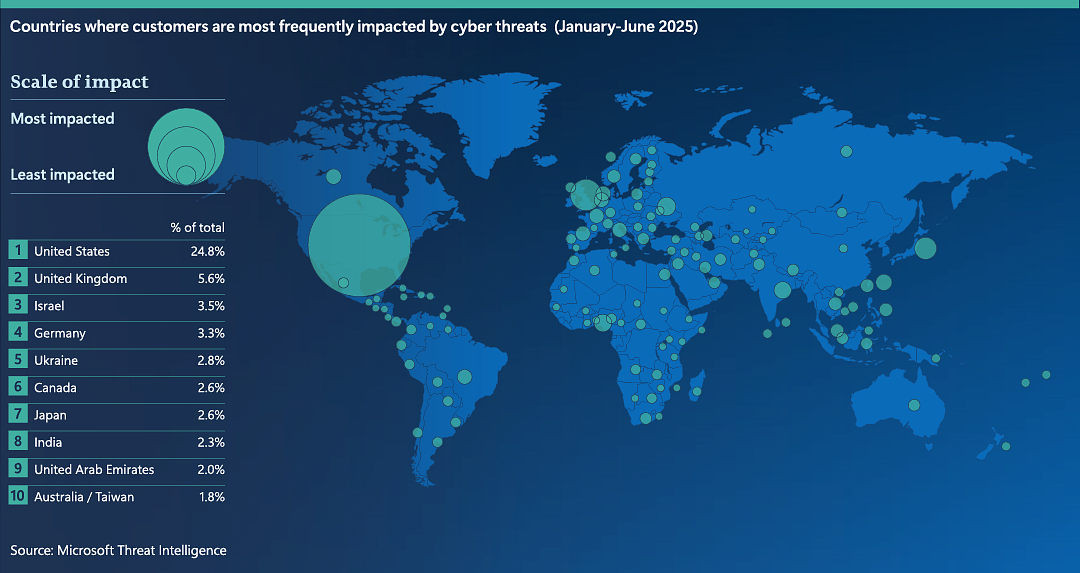

Israel, UAE and US among top cyber targets for Iran, Microsoft report says: Tehran shows no sign of slowing cyber attack efforts, according to analysis
thenationalnews.com/future/technology/2025/10/16/iran-cyberattacks-israel-us-uae/
New HybridPetya ransomware can bypass UEFI Secure Boot: A recently discovered ransomware strain called HybridPetya can bypass the UEFI Secure Boot feature to ...
bleepingcomputer.com/news/security/new-hybridpetya-ransomware-can-bypass-uefi-secure-boot/

'Microsoft has become like an arsonist selling firefighting services to their victims' says US senator, referring it to the FTC for a cybersecurity ...
pcgamer.com/software/security/microsoft-has-become-like-an-arsonist-selling-firefighting-services-to-their-victims-says-us-senator-referring-it-to-the-ftc-for-a-cybersecurity-flaw-though-microsoft-says-it-has-a-plan/

Senator urges FTC to probe Microsoft for "gross cybersecurity negligence"
techspot.com/news/109443-senator-urges-ftc-probe-microsoft-gross-cybersecurity-negligence.html

158-year-old company forced to close after ransomware attack precipitated by a single guessed password — 700 jobs lost after hackers demand unpayable sum
tomshardware.com/tech-industry/cyber-security/158-year-old-company-forced-to-close-after-ransomware-attack-precipitated-by-a-single-guessed-password-700-jobs-lost-after-hackers-demand-unpayable-sum


Microsoft SharePoint Flaw Is Being Abused to Spread Ransomware: It's not just data theft. A China-based hacking group is using a flaw in vulnerable SharePoint ...
uk.pcmag.com/security/159288/microsoft-sharepoint-flaw-is-being-abused-to-spread-ransomware


‘Octo Tempest’ hacking group now targeting aviation industry, Microsoft says: The group, also known as 'Scattered Spider' and linked to high-profile cyberattacks ...
ynetnews.com/business/article/by8zgcuull
Microsoft: Vanilla Tempest hackers hit healthcare with INC ransomware: Microsoft says a ransomware affiliate it tracks as Vanilla Tempest now targets U.S ...
bleepingcomputer.com/news/microsoft/microsoft-vanilla-tempest-hackers-hit-healthcare-with-inc-ransomware/
Next