program that locks files until a sum of money is paid

CISA: SafePay ransomware hit over 600 critical infrastructure orgs: The Cybersecurity and Infrastructure Security Agency (CISA) says the SafePay ransomware gang ...
bleepingcomputer.com/news/security/cisa-and-fbi-safepay-ransomware-has-hit-over-600-critical-infrastructure-organizations/

Authorities disrupt nearly 11,000 cybercrime networks in Africa: Law enforcement agencies have disrupted nearly 11,000 cybercriminal networks and arrested more ...
bleepingcomputer.com/news/security/authorities-disrupt-nearly-11-000-cybercrime-networks-in-africa/


Hackers steal children's data after company used 'Password1' for old account: The data watchdog reprimanded Ogi Networks Limited and Data Cymru after the 2024 ...
bbc.co.uk/news/articles/c6r7y03e9m3ro


dlvr.it Oct 20
Palo Alto's firewall OS has been under attack from multiple ransomware groups since June
theregister.com/cyber-crime/2026/10/20/palo-altos-firewall-os-has-been-under-attack-from-multiple-ransomware-groups-since-june/5304226

Germany arrests alleged core Qilin ransomware member after extradition: Germany has arrested a Russian national suspected of being a leading member of the Qilin ...
bleepingcomputer.com/news/security/germany-arrests-alleged-core-qilin-ransomware-member-after-extradition/
Engineer sentenced for locking over 3,000 devices on employer network: A former core infrastructure engineer at an industrial company headquartered in New Jersey ...
bleepingcomputer.com/news/security/engineer-sentenced-for-locking-thousands-of-devices-on-employer-network/


CyberNews Oct 09
Prosecutors charged MonsterCloud owner Zohar Pinhasi with defrauding ransomware victims. Read more: cnews.link

Ransomware recovery firm claimed it could decrypt files, but may have just paid hackers and pocketed the difference
techspot.com/news/114137-ransomware-recovery-firm-claimed-could-decrypt-files-but.html

Advantest confirms personal information stolen in ransomware attack: Advantest Corporation is notifying affected individuals that a ransomware attack earlier ...
bleepingcomputer.com/news/security/advantest-confirms-personal-information-stolen-in-ransomware-attack/

Trump Mobile hacked and this shows how ridiculously few there are: The ransomware group BYOD has published personal data of 3,615 customers (apparently all of ...
winfuture.de/news,161820.html


Shock and surprise after FBI arrests Canadian cybersecurity expert in ShinyHunters hacking case
cbc.ca/news/canada/canadian-cybersecurity-expert-arrested-fbi-shinyhunters-9.7378256


Canadian ransomware negotiator arrested amid FBI hacker crackdown: A Canadian ransomware negotiator was arrested Thursday and faces unspecified extortion charges ...
cp24.com/news/canada/2026/10/13/canadian-ransomware-negotiator-arrested-amid-fbi-hacker-crackdown/
dlvr.it Oct 14
Ransomware gets personal: 'We-know-where-you-are kind of stuff': 37% of ransomware attacks involve psychological or physical threats, global survey found
theregister.com/cyber-crime/2026/10/14/ransomware-gets-personal-we-know-where-you-are-kind-of-stuff/5302939

Warlock ransomware breach SharePoint in water, telecom operator attacks: The China-linked ransomware group Warlock targeted a water utility, a telecom provider ...
bleepingcomputer.com/news/security/warlock-ransomware-breach-sharepoint-in-water-telecom-operator-attacks/
Ransomware attack disrupts Japan's IDCF Cloud used by govt clients: IDC Frontier, a major Japanese cloud and digital infrastructure company ...
bleepingcomputer.com/news/security/ransomware-attack-disrupts-japans-idcf-cloud-used-by-govt-clients/
dlvr.it Oct 02
Teen suspected of running KillSec ransomware group as cops seize servers, arrest three
theregister.com/cyber-crime/2026/10/02/teen-suspected-of-running-killsec-ransomware-group-as-cops-seize-servers-arrest-three/5300784

FBI: Ongoing FortiBleed attacks lock out FortiGate VPN admins: The FBI is warning that FortiBleed attacks are still ongoing, targeting exposed Fortinet FortiGate ...
bleepingcomputer.com/news/security/fbi-ongoing-fortibleed-attacks-lock-out-fortigate-vpn-admins/

Russian ransomware developer arrested: Access to "snake" during vacation in Japan
spiegel.de/panorama/cyberkriminalitaet-mutmasslicher-ransomware-entwickler-in-japan-festgenommen-a-edbdbfc5-52de-4ea6-a789-10f0bf27664f


How to Build Ransomware Defense and Data Governance Into Your AI Storage From Day One
pcmag.com/articles/how-to-build-ransomware-defense-and-data-governance-into-your-ai-storage


The Insider Oct 08
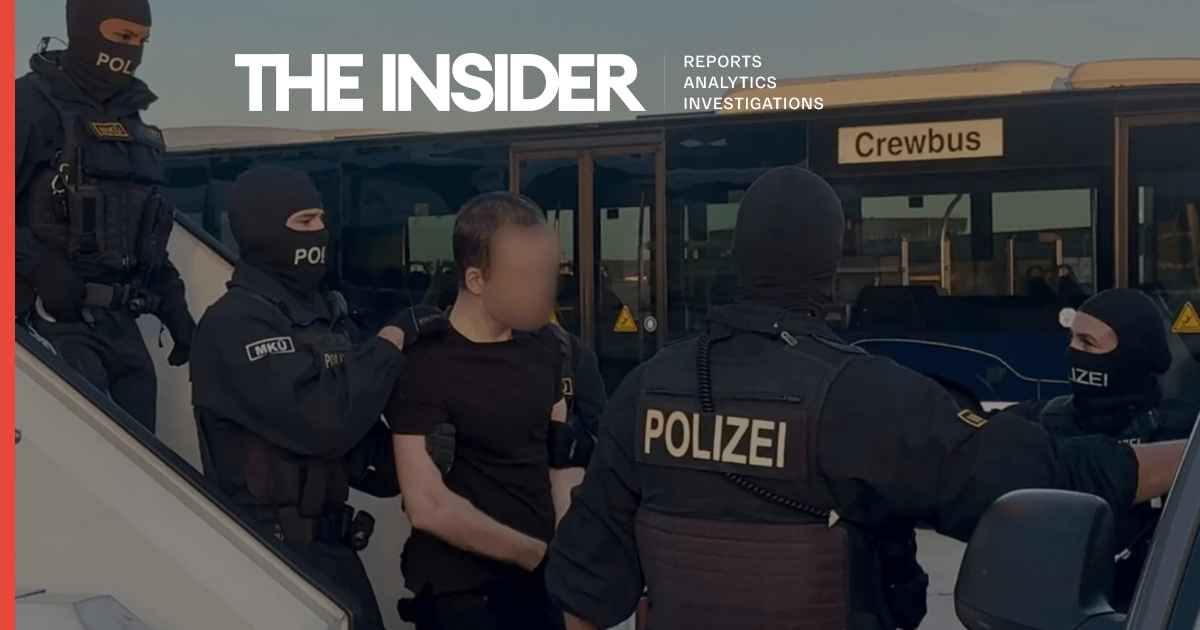
Japan extradites Russian man to Germany over role in Qilin ransomware group: Japan extradited 28-year-old Russian national Vladimir K. to Germany ...
theins.press/en/news/298060
dlvr.it Oct 07
FortiBleed still a bleeding nuisance as FBI confirms ongoing attacks: Tens of thousands more victims and more ransomware groups getting in on the act
theregister.com/security/2026/10/07/fortibleed-still-a-bleeding-nuisance-as-fbi-confirms-ongoing-attacks/5301585
JadePuffer agentic AI attacks target Azure, destroy cloud resources: The JadePuffer ransomware operator is targeting Azure tenants with agent-driven attacks that ...
bleepingcomputer.com/news/security/jadepuffer-agentic-ai-attacks-target-azure-destroy-cloud-resources/
Japan's Keio confirms ransomware attack disrupted business systems: Keio Corporation (Keio), a major private railway operator in Japan, said its network was ...
bleepingcomputer.com/news/security/japans-keio-confirms-ransomware-attack-disrupted-business-systems/
Ransomware uses AI agents to specifically devastate Azure environments: A ransomware group has begun to specifically devastate Azure environments with AI-powered ...
winfuture.de/news,161607.html


WIRED Sep 12
From Hacks to Bioweapons, Claude Misuse Is Now Everywhere: Plus: The US disrupts the internet's biggest black market, a Conti ransomware hacker gets prison time ...
wired.com/story/security-news-this-week-from-hacks-to-bioweapons-claude-misuse-is-now-everywhere/

Hacker-on-Hacker Crime: ShinyHunters Is Trying to Extort CLOP Ransomware Group: Cybercriminal group ShinyHunters claims to have hijacked the website of a rival ...
pcmag.com/news/hacker-on-hacker-crime-shinyhunters-is-trying-to-extort-clop-ransomware

Ryuk ransomware member sentenced to 24 months in prison: An Armenian man was sentenced to 24 months in prison and 3 years of supervised release for hacking U.S ...
bleepingcomputer.com/news/security/ryuk-ransomware-member-sentenced-to-24-months-in-prison/
CISA: Ransomware gangs now exploiting critical TeamCity flaw: The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned federal agencies on ...
bleepingcomputer.com/news/security/cisa-ransomware-gangs-now-exploiting-critical-teamcity-flaw/
CISA: Critical VMware RCE flaw now exploited by ransomware gangs: The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned security teams that ...
bleepingcomputer.com/news/security/cisa-critical-vmware-vcenter-rce-flaw-now-exploited-by-ransomware-gangs/
CISA: WatchGuard RCE flaw now exploited in ransomware attacks: The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that ransomware ...
bleepingcomputer.com/news/security/cisa-watchguard-rce-flaw-now-exploited-in-ransomware-attacks/
Rhysida ransomware attack: Hackers apparently publish more than one million Berlin data records
spiegel.de/netzwelt/berlin-hacker-veroeffentlichen-offenbar-mehr-als-eine-million-daten-a-25fd53b1-c525-42f7-a6f1-0137569bbdb8


German police call Vitaly Kovalev a founder of Trickbot, the hacking group whose ransomware hit U.S. hospitals. New People had him on its Duma candidate list ...
meduza.io/en/news/2026/09/18/germany-suspects-vitaly-kovalev-of-founding-the-hacking-group-behind-trickbot-whose-ransomware-hit-u-s-hospitals-now-the-new-people-party-has-made-him-a-candidate-for-russia-s-parliament
Berlin confirms data theft after Rhysida ransomware attack claims: Berlin's city administration has confirmed that cybercriminals are attempting to extort ...
bleepingcomputer.com/news/security/berlin-confirms-data-theft-after-rhysida-ransomware-attack-claims/
New Android malware encrypts files, steals data, and harasses victims: A new Android malware strain called Mantax Otax combines ransomware and spyware ...
bleepingcomputer.com/news/security/new-android-malware-encrypts-files-steals-data-and-harasses-victims/
Veradigm warns of patient data breach after ransomware gang claims attack: Healthcare technology company Veradigm disclosed a data breach after a cybersecurity ...
bleepingcomputer.com/news/security/veradigm-discloses-patient-data-breach-after-gentlemen-gang-claims-attack/

Berlin being ‘blackmailed’ after cyberattack: mayor: Rhysida notably claimed responsibility for a ransomware attack against the British Library in 2023 and ...
ctvnews.ca/world/article/berlin-being-blackmailed-after-cyberattack-mayor/
dlvr.it Sep 02
AI agents carried out every step of this ransomware attack – then left the victim an 80-page security audit
theregister.com/security/2026/09/02/ai-agents-carried-out-every-step-of-this-ransomware-attack-then-left-the-victim-an-80-page-security-audit/5294009

dlvr.it Sep 01
The Gentlemen come calling as Nutex confirms sensitive data theft: Ransomware crew threatens publication while healthcare biz assesses which records escaped
theregister.com/cyber-crime/2026/09/01/the-gentlemen-come-calling-as-nutex-confirms-sensitive-data-theft/5293642

July was the worst month for ransomware victim claims in 2026 - or was it?: We shouldn't ignore agentic AI ransomware threats, but the claims of a new ransomware ...
zdnet.com/article/ransomware-july-victim-count-spiked-in-july-but-whats-behind-it/

dlvr.it Aug 20
Ransomware crook poses as recovery firm to steal payments from fellow extortionists
theregister.com/cyber-crime/2026/08/20/ransomware-crook-poses-as-recovery-firm-to-steal-payments-from-fellow-extortionists/5290344


30 Bitcoin or Leak - | Ransomware gang extorts Berlin: The group "Rhysida" wants 30 Bitcoins from Berlin or the publication of confidential data ...
heise.de/news/30-Bitcoin-oder-Leak-Ransomware-Bande-erpresst-Berlin-11434325.html

Rogue ransomware affiliate poses as data recovery firm to steal payments: A suspected ransomware affiliate is posing as a ransomware recovery service called ...
bleepingcomputer.com/news/security/rogue-ransomware-affiliate-ransom-busters-poses-as-data-recovery-firm/
CISA: Windows Task Host flaw now exploited by ransomware gangs: The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that ransomware ...
bleepingcomputer.com/news/security/cisa-windows-task-host-flaw-now-exploited-by-ransomware-gangs/
The Best Antivirus Software for 2026: Antivirus apps protect your PC's personal information, data, bank accounts, and other sensitive information ...
pcmag.com/picks/the-best-antivirus-protection

Philips and GE investigating Clop ransomware data theft claims: Tech giants General Electric (GE) and Philips have also confirmed they're investigating ...
bleepingcomputer.com/news/security/philips-and-ge-investigating-clop-ransomware-data-theft-claims/
CISA: Microsoft SharePoint flaw now exploited in ransomware attacks: CISA confirmed today that ransomware gangs have begun abusing a high-severity Microsoft ...
bleepingcomputer.com/news/security/cisa-microsoft-sharepoint-flaw-now-exploited-in-ransomware-attacks/
dlvr.it Aug 27
CRPx0 hacking service for dummies claims victim count more than quintupled: It's 'built to be operated by a human with no technical background'
theregister.com/cyber-crime/2026/08/27/crpx0-hacking-service-for-dummies-claims-victim-count-more-than-quintupled/5293097
CISA: SonicWall SMA1000 flaws now exploited by ransomware gangs: CISA has confirmed that ransomware gangs have begun exploiting two recently patched SonicWall ...
bleepingcomputer.com/news/security/cisa-sonicwall-sma1000-flaws-now-exploited-by-ransomware-gangs/
Clop created custom web shell for Windchill data theft attacks: A custom Java web shell likely linked to the Clop ransomware gang was designed specifically for ...
bleepingcomputer.com/news/security/clop-created-custom-web-shell-for-windchill-data-theft-attacks/
New StormEncryptor ransomware used by former Medusa affiliate: A financially motivated threat actor previously associated with the Medusa ransomware operation is ...
bleepingcomputer.com/news/security/new-stormencryptor-ransomware-used-by-former-medusa-affiliate/
Shell investigates 'potential incident' after Clop data theft claims: Oil giant Shell has confirmed it is investigating a potential security incident ...
bleepingcomputer.com/news/security/shell-investigates-potential-incident-after-clop-data-theft-claims/
Akira hackers disable EDR with Safe Mode, steal data but fail to encrypt: An Akira ransomware affiliate disabled the endpoint detection and response (EDR) ...
bleepingcomputer.com/news/security/akira-hackers-disable-edr-with-safe-mode-steal-data-but-fail-to-encrypt/
DeadLock ransomware uses blockchain to resist infrastructure takedown: The DeadLock ransomware operation is using a decentralized infrastructure that relies on ...
bleepingcomputer.com/news/security/deadlock-ransomware-uses-blockchain-to-resist-infrastructure-takedown/
dlvr.it Aug 09
Ransomware gangs skip the CEO, head straight for the 40-something IT manager: Gen Xers who feel triggered by this should remember to unplug the network cable and ...
theregister.com/security/2026/08/09/ransomware-gangs-skip-the-ceo-head-straight-for-the-40-something-it-manager/5284499
dlvr.it Aug 21
SickKids children’s hospital bandages up careers website after intruder breaks in
theregister.com/cyber-crime/2026/08/21/sickkids-childrens-hospital-bandages-up-careers-website-after-intruder-breaks-in/5291098
Microsoft Teams vishing attacks lead to Chaos ransomware attacks: Threat actors are impersonating IT support staff in Microsoft Teams calls to gain remote access ...
bleepingcomputer.com/news/security/microsoft-teams-vishing-attacks-lead-to-chaos-ransomware-attacks/
Ransom Cartel ransomware creator sentenced to 16 years in prison: Maksim Silnikau, the creator and administrator of the Ransom Cartel ransomware operation ...
bleepingcomputer.com/news/security/ransom-cartel-ransomware-creator-sentenced-to-16-years-in-prison/