
Google helps devs bring new Android features to older phones:
A new tool will help developers find out which phones support which features
androidpolice.com/google-devs-new-android-features-older-phones-extension-sdk/
Story Details
| Last Updated | |
| Total Articles | 5 |
Main Topics


operating system created by Google for use on mobile devices
News on this topic

Attack on paramedics in Vohwinkel: Rescue workers are not safe from attacks in Wuppertal either. This is shown by an incident yesterday, Monday (January 9) ...
wuppertal-total.de/blaulicht/angriff-auf-sanitaeter-in-vohwinkel/

Android, iPhone users defrauded from fake AI apps - Punch Newspapers
punchng.com/android-iphone-users-defrauded-from-fake-ai-apps/

Hackers target Android users with fake Shagle video-chat app: The StrongPity APT hacking group is distributing a fake Shagle chat app that is a trojanized ...
bleepingcomputer.com/news/security/hackers-target-android-users-with-fake-shagle-video-chat-app/
More articles on this subject
Previous
Android 13 QPR2 Beta 2 can force-theme all icons on your home screen: Finally, a consistently themed home screen
androidpolice.com/android-13-qpr2-beta-2-force-themed-icons/
Next
Similar to This
Previous

How To Clear The Cache On Your Android Device: Your apps and browsers may be overdue for some tidying up.
engadget.com/2300269/how-to-clear-cache-android/


Quick Share will soon come directly to third-party Android and iPhone apps: Google will soon let developers integrate Quick Share directly into third-party ...
sammobile.com/news/quick-share-come-third-party-android-iphone-apps/

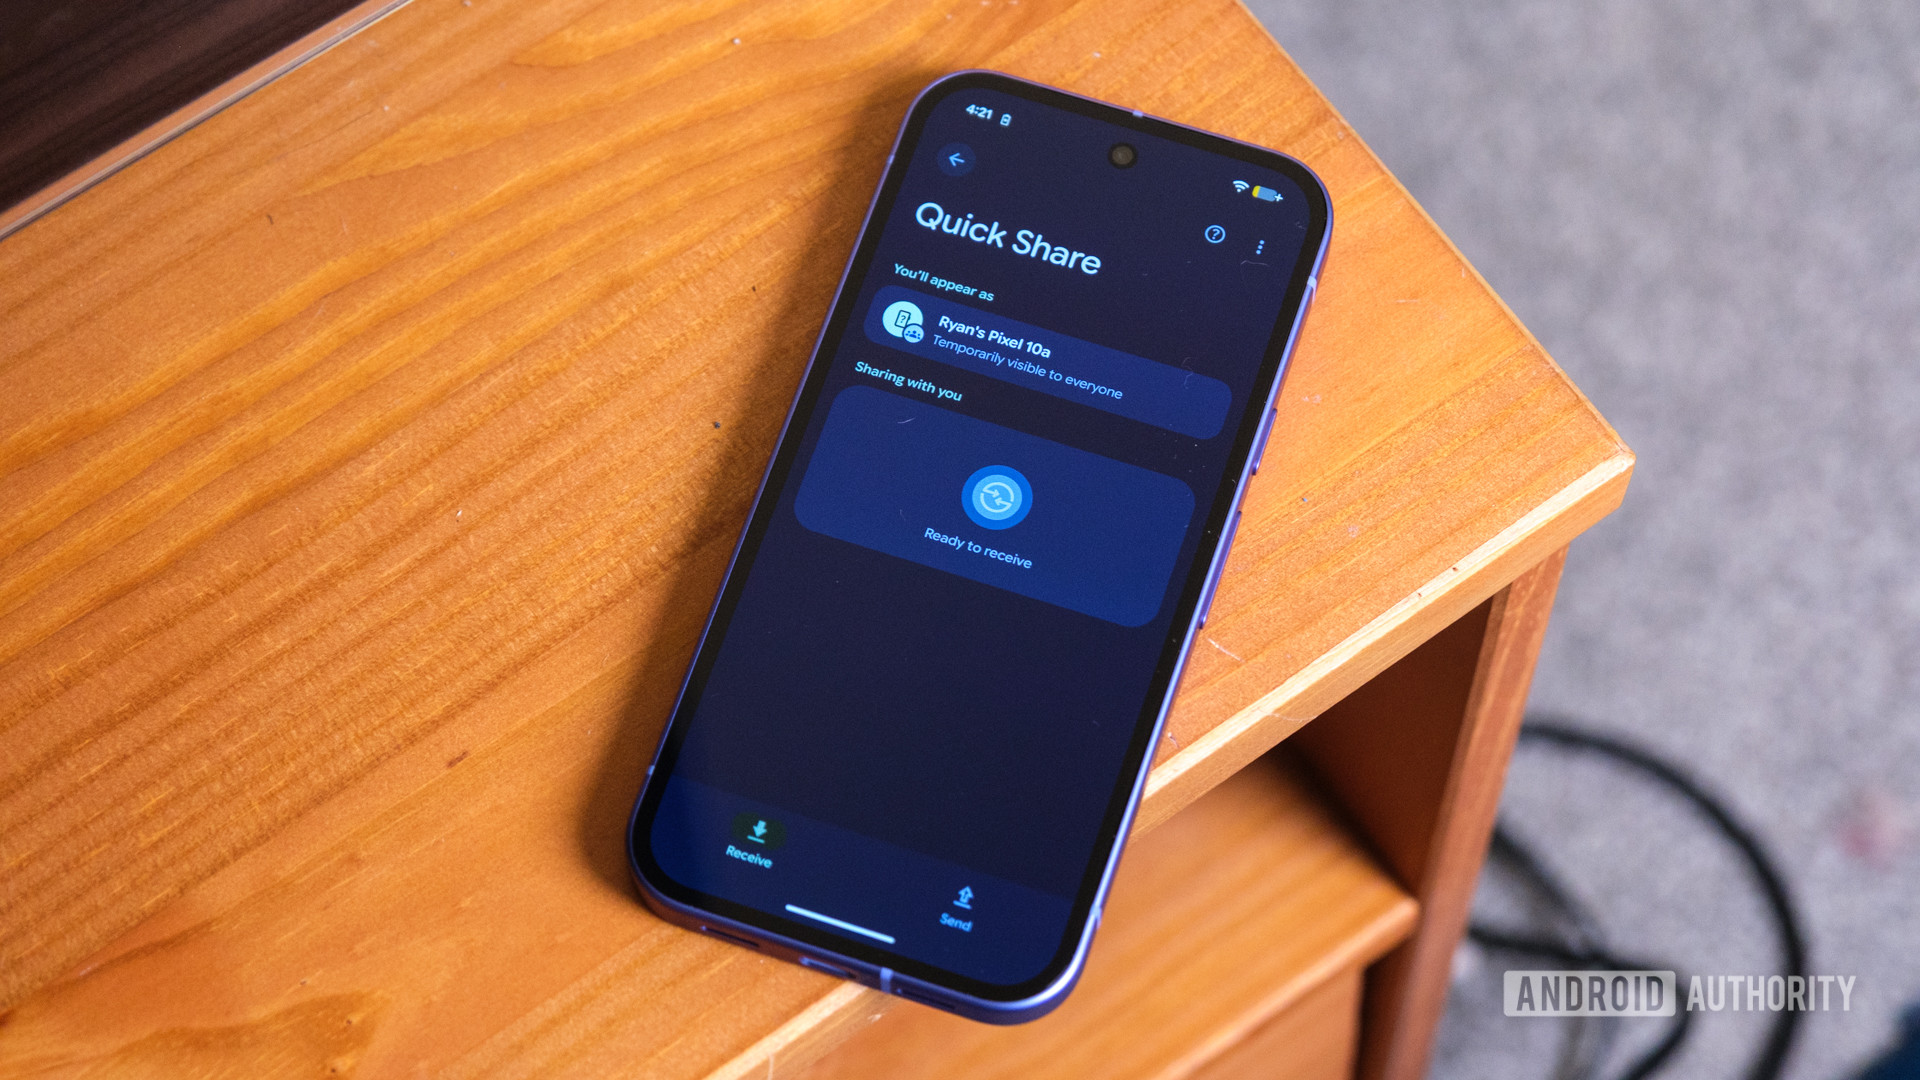
Quick Share will soon work directly in Android and iOS apps: Google will launch a Quick Share SDK for Android and iOS apps, which will let developers integrate ...
androidauthority.com/quick-share-sdk-launch-time-frame-3730882/
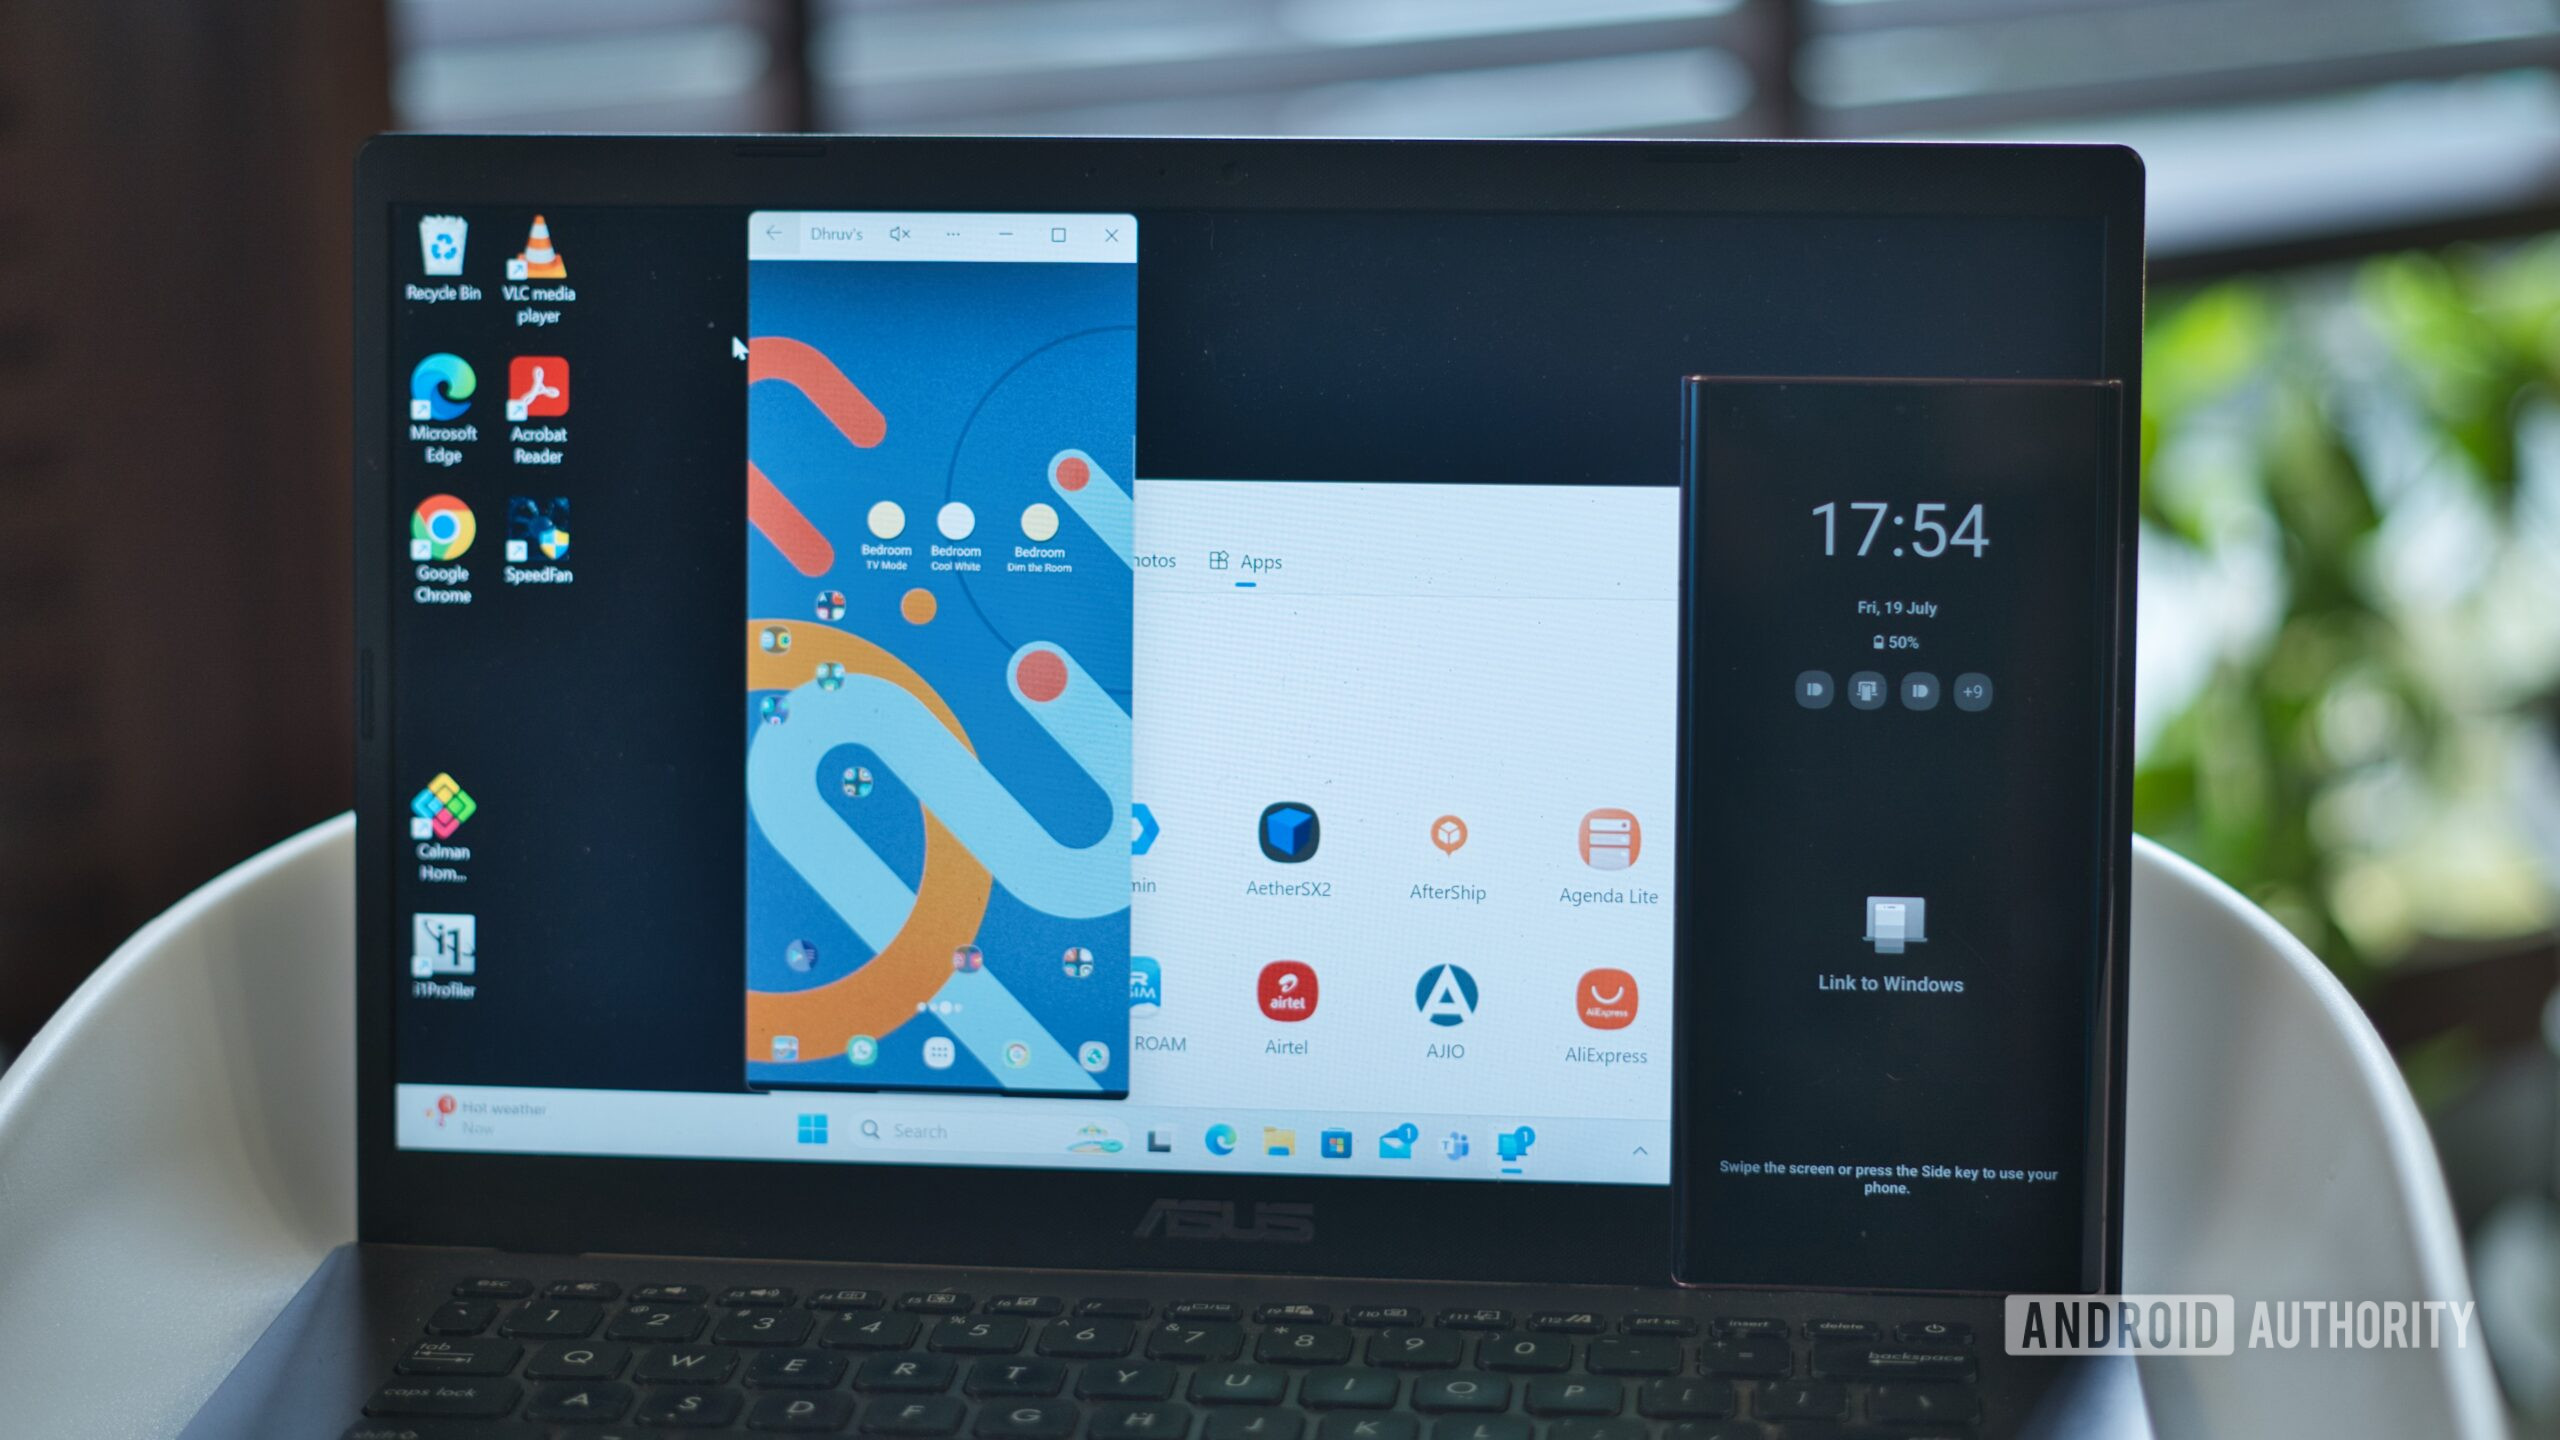
Windows 11 now lets you access Android apps straight from Search: Microsoft has rolled out a new Windows 11 build that makes opening Android phone apps on PC ...
androidauthority.com/windows-11-search-android-app-actions-3730729/

Midnight Mimosa malware is preinstalled on cheap Android phones: Midnight Mimosa malware is preinstalled on some low-cost Android phones, giving attackers ...
androidpolice.com/this-android-malware-can-reach-your-phone-before-you-ever-use-it/

I turned my non-Pixel Android into a Pixel clone to unlock these exclusive features
androidpolice.com/pixelify-your-android-phone/

Before downloading a new Play Store app or game, here's every red flag you should check for
androidpolice.com/play-store-app-verification/

Mac.apk runs my favorite Android apps on my Mac; most just worked: Forget emulators: this free Mac app runs Android apps like native software
androidpolice.com/macapk-runs-my-favorite-android-apps-on-my-mac-and-most-just-worked/

BTMOB Android malware service generates custom phishing payloads: An Android remote access trojan named BTMOB is offered to cybercriminals with a builder ...
bleepingcomputer.com/news/security/btmob-android-malware-service-generates-custom-phishing-payloads/
Scam Android apps on Google Play got millions of downloads from a creepy pitch: Scam Android apps on dubbed CallPhantom claimed they could reveal private call ...
androidauthority.com/callphantom-scam-android-apps-3665212/

Google just wiped 9 million Android devices from a secret chinese proxy network: Dubbed "residential proxy networks", Ipidea used apps installed on all ...
indianexpress.com/article/technology/tech-news-technology/google-android-ipidea-chinese-proxy-network-shut-down-10504897/


Hundreds of malicious Android apps exploited to drive "SlopAds" massive ad fraud
techspot.com/news/109522-hundreds-malicious-android-apps-exploited-drive-slopads-massive.html

Vicious Crocodilus Malware Has Evolved And It's Bad News For Android Users: The Crocodilus malware first appeared back in March, and researchers are already ...
hothardware.com/news/crocodilus-malware-bad-news-for-android-users

Android malware steals payment card data using previously unseen technique: Attacker then emulates the card and makes withdrawals or payments from victim's ...
arstechnica.com/security/2024/08/android-malware-uses-nfc-to-read-payment-card-data-then-sends-it-to-attacker/

on.mash.to Aug 01 24

Android users, beware! Text message stealing malware is targeting smartphones to gain access to users' data
mashable.com/article/android-malware-sms-stealer-campaign
More Android apps riddled with malware spotted on Google Play: An Android remote access trojan (RAT) known as VajraSpy was found in 12 malicious applications ...
bleepingcomputer.com/news/security/more-android-apps-riddled-with-malware-spotted-on-google-play/

This app makes Android phones unusable by sending fake Bluetooth requests: Bluetooth-LE-Spam is an Android app that can spam Android devices with fake Bluetooth ...
indianexpress.com/article/technology/tech-news-technology/this-app-makes-android-phones-unusable-by-sending-fake-bluetooth-requests-9008853/
Hackers steal Signal, WhatsApp user data with fake Android chat app: Hackers are using a fake Android app named 'SafeChat' to infect devices with ...
bleepingcomputer.com/news/security/hackers-steal-signal-whatsapp-user-data-with-fake-android-chat-app/
Key FactsHackers steal Signal and WhatsApp user data using fake Android chat app
Jul 31, 2023 · Reading time: ~30 sec.
Summary created with AI assistance · Source: bleepingcomputer.com
Summary created with AI assistance · Source: bleepingcomputer.com
- The Android spyware is suspected to be a variant of 'Coverlm,' which steals data from communication apps like Telegram, Signal, WhatsApp, Viber, and Facebook Messenger.
- CYFIRMA analysts note TTP similarities to another Indian state-sponsored threat group, the 'DoNot APT' (APT-C-35), which has previously infected Google Play with fake chat apps acting as spyware.
- ESET reported last year that the Bahamut group was using fake VPN apps for the Android platform that included extensive spyware functions.
- The analysts report that Safe Chat features a deceptive interface that makes it appear as a real chat app and guides the victim through a seemingly legitimate user registration process, adding credibility and serving as excellent cover for the spyware.
Next