
Hackers exploit SSHole OpenSSH flaw to breach Linux systems:
Hackers are actively exploiting the "SSHole" vulnerability (CVE-2026-123158) in OpenSSH ...
bleepingcomputer.com/news/security/hackers-exploit-sshole-openssh-flaw-to-breach-linux-systems/
Story Details
| Last Updated | |
| Total Articles | 2 |
Main Topics

software, data or commands that use a bug or vulnerability to compromise a computer system

any attempt to expose, alter, disable, destroy, steal or gain unauthorized access to or make unauthorized use of a computer system
Similar to This
Previous


Vulnerability that lets hackers SSH into Linux devices is under active exploitation
arstechnica.com/security/2026/11/vulnerability-that-lets-hackers-ssh-into-linux-devices-is-under-active-exploitation/

CyberNews Nov 10
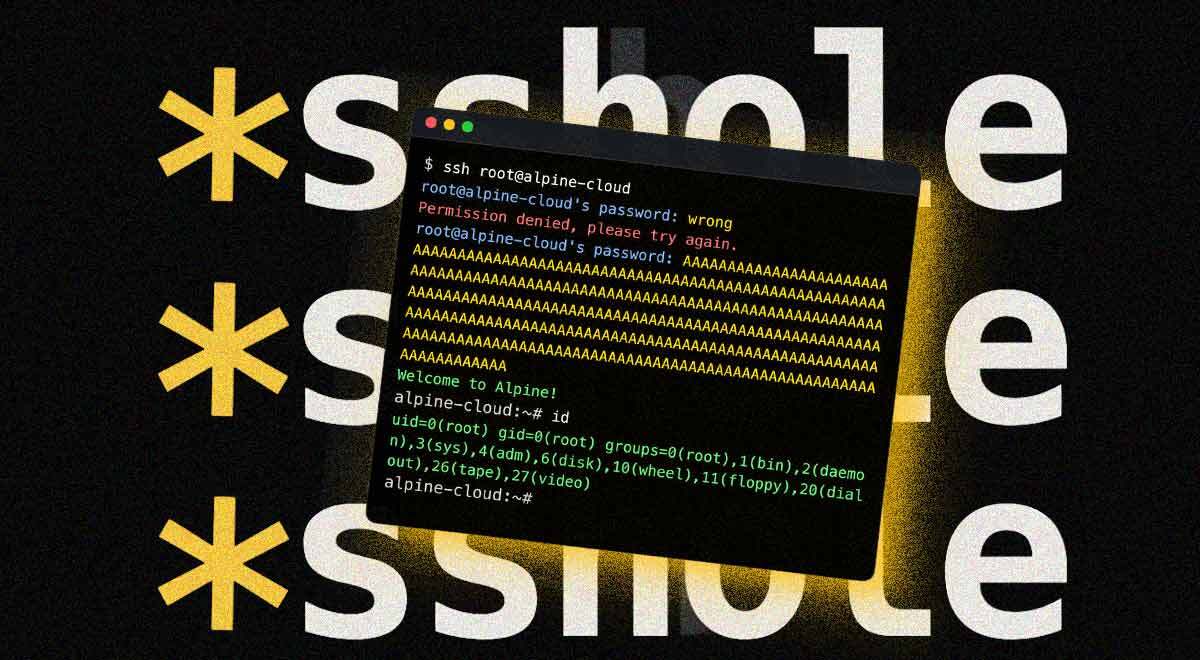
SSHole Linux login flaw actively exploited: any password over 256 characters works
cybernews.com/security/cisa-confirms-active-exploitation-sshole/
Meet *sshole, the vulnerability that lets hackers SSH into Linux devices: Certain configurations of Alpine are affected. Other distros may be as well.
arstechnica.com/security/2026/11/vulnerability-allows-attackers-to-log-into-some-linux-devices-sans-password/
OpenSSH flaw lets attackers log into password-disabled Linux accounts: A newly disclosed OpenSSH vulnerability dubbed "*sshole" allows attackers to log ...
bleepingcomputer.com/news/security/openssh-flaw-lets-attackers-log-into-password-disabled-linux-accounts/

Windows has a hidden, free SSH server, and I manage every PC in my house from one terminal now
xda-developers.com/windows-has-a-built-in-ssh-server/

github.com Oct 21

GitHub - abruption/dots-tailscale: User-level Tailscale and OpenSSH setup for ChatGPT Dots cloud computers
github.com/abruption/dots-tailscale

The New Stack Oct 08

OpenSSH 10.6 deliberately breaks two features in the name of security: OpenSSH 10.6 weakens SSH compression and rejects $ and in command-line usernames to close ...
thenewstack.io/openssh-breaks-compression-usernames/
Next