
After a row with Microsoft: Researcher leaks zero-day exploit for BitLocker - | Golem.de
golem.de/news/nach-zoff-mit-microsoft-forscher-leakt-zero-day-exploit-fuer-bitlocker-2605-208630.html

Story Details
| Last Updated | |
| Total Articles | 1 |
Main Topics


software, data or commands that use a bug or vulnerability to compromise a computer system
Similar to This
Previous

Windows 11 quietly encrypted your entire PC, and one firmware update can lock you out of everything
xda-developers.com/windows-11-quietly-encrypted-your-entire-pc-and-one-firmware-update-can-lock-you-out-of-everything/
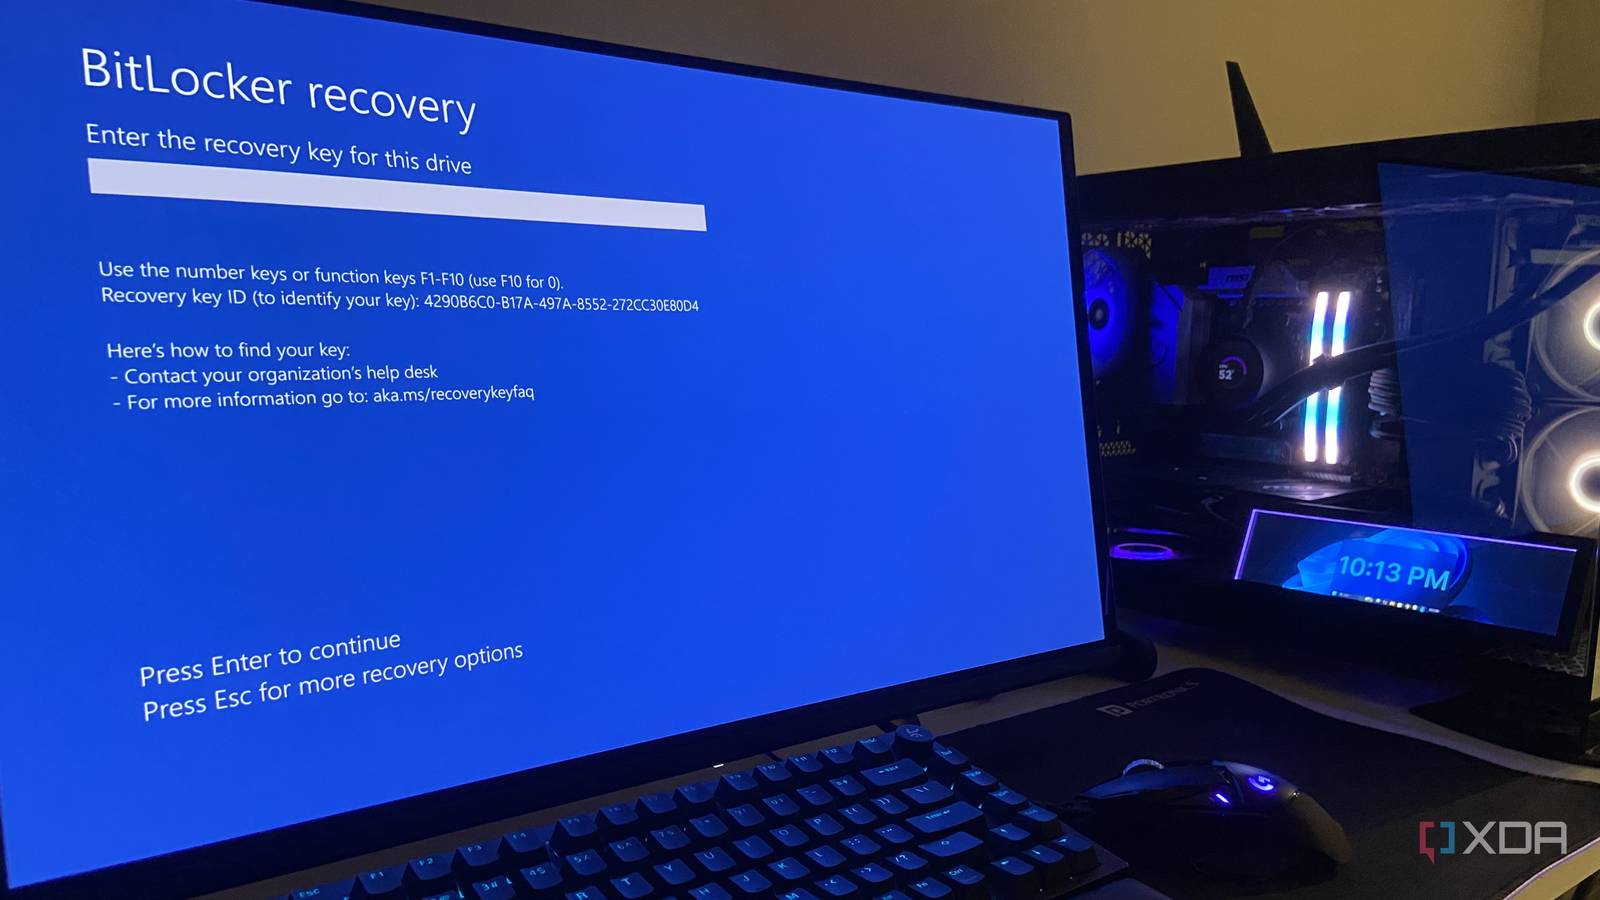
Key FactsWindows 11 Device Encryption Can Trigger Unexpected Recovery Lockouts
Sep 14, 2026 · Reading time: ~45 sec.
Summary created with AI assistance · Source: xda-developers.com
Summary created with AI assistance · Source: xda-developers.com
- Since October 2024, Windows 11 24H2 has enabled Device Encryption by default on many clean installs and resets.
- For local accounts, Microsoft says the recovery key is not automatically saved when the device is encrypted.
- BIOS or UEFI updates, TPM changes, and boot-manager modifications can reportedly trigger the 48-digit key prompt.
- Users should save the key before changing Secure Boot or the TPM and suspend BitLocker during those changes.
I've argued time and again that many of the default settings and updates that Windows 11 ships with assume the best interests of the user, but in practice, they can backfire and cause them genuine harm and loss.— Abhinav, author of the article

Disgruntled security researcher just dropped another Windows zero-day, right on schedule
techspot.com/news/113477-disgruntled-security-researcher-dropped-another-windows-zero-day.html

Windows Vulnerability: Hacker Outsmarts Microsoft with Ninth Zero-Day Exploit: The conflict between the 'security researcher' Nightmare Eclipse and ...
winfuture.de/news,160026.html


Nightmare-Eclipse Drops Another BitLocker Bypass After YellowKey Patch: Nightmare-Eclipse, the current bane of Microsoft's existence, strike again with new ...
hothardware.com/news/nightmare-eclipse-drops-another-bitlocker-bypass-after-yellowkey-patch
Nightmare Eclipse claims to have found another BitLocker vulnerability: Security researcher "Nightmare Eclipse" has struck again, publishing information about a ...
winfuture.de/news,159287.html

Windows BitLocker exploit sparks messy feud between Microsoft and the researcher who exposed it
techspot.com/news/112576-windows-bitlocker-exploit-sparks-messy-feud-between-microsoft.html

WindowsCentral May 28
"I have proof for every single word": This security researcher's GitHub and Microsoft accounts were deleted after claiming a Windows 11 exploit ...
windowscentral.com/microsoft/security-researcher-github-microsoft-accounts-deleted-windows-11-exploit-bitlocker
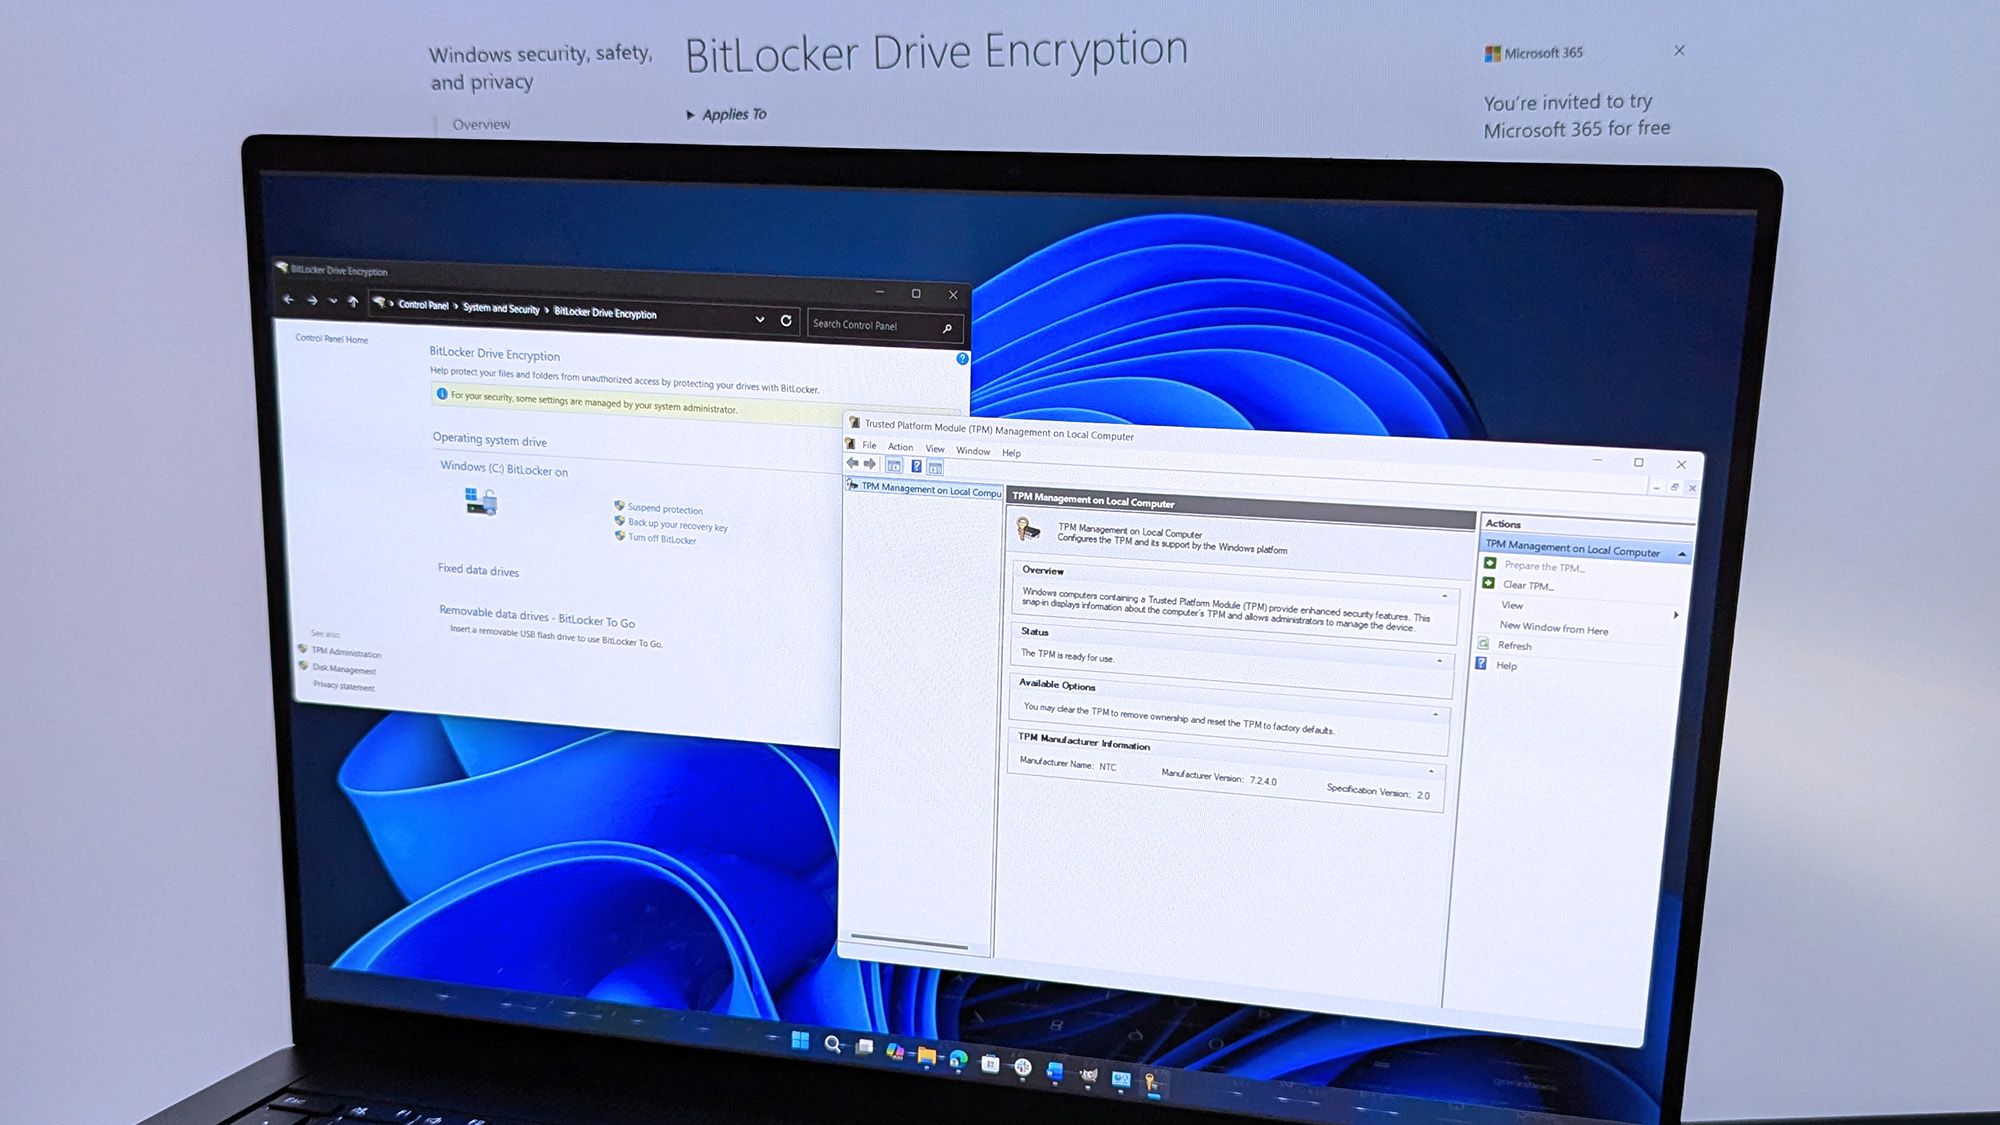
Microsoft Mitigates Dangerous YellowKey Tool That Breaks BitLocker: Microsoft has a potential workaround for the recent YellowKey BitLocker exploit ...
hothardware.com/news/microsoft-mitigates-dangerous-yellowkey-tool-that-breaks-bitlocker
YellowKey: Another BitLocker backdoor - | Is this one from Microsoft?: Another vulnerability has been found that can bypass Microsoft's BitLocker encryption ...
winfuture.de/news,158701.html

A new Windows 11 BitLocker bypass only needs a USB stick, and the researcher thinks it's a backdoor
xda-developers.com/new-windows-11-bitlocker-bypass-needs-usb-stick-researcher-backdoor/
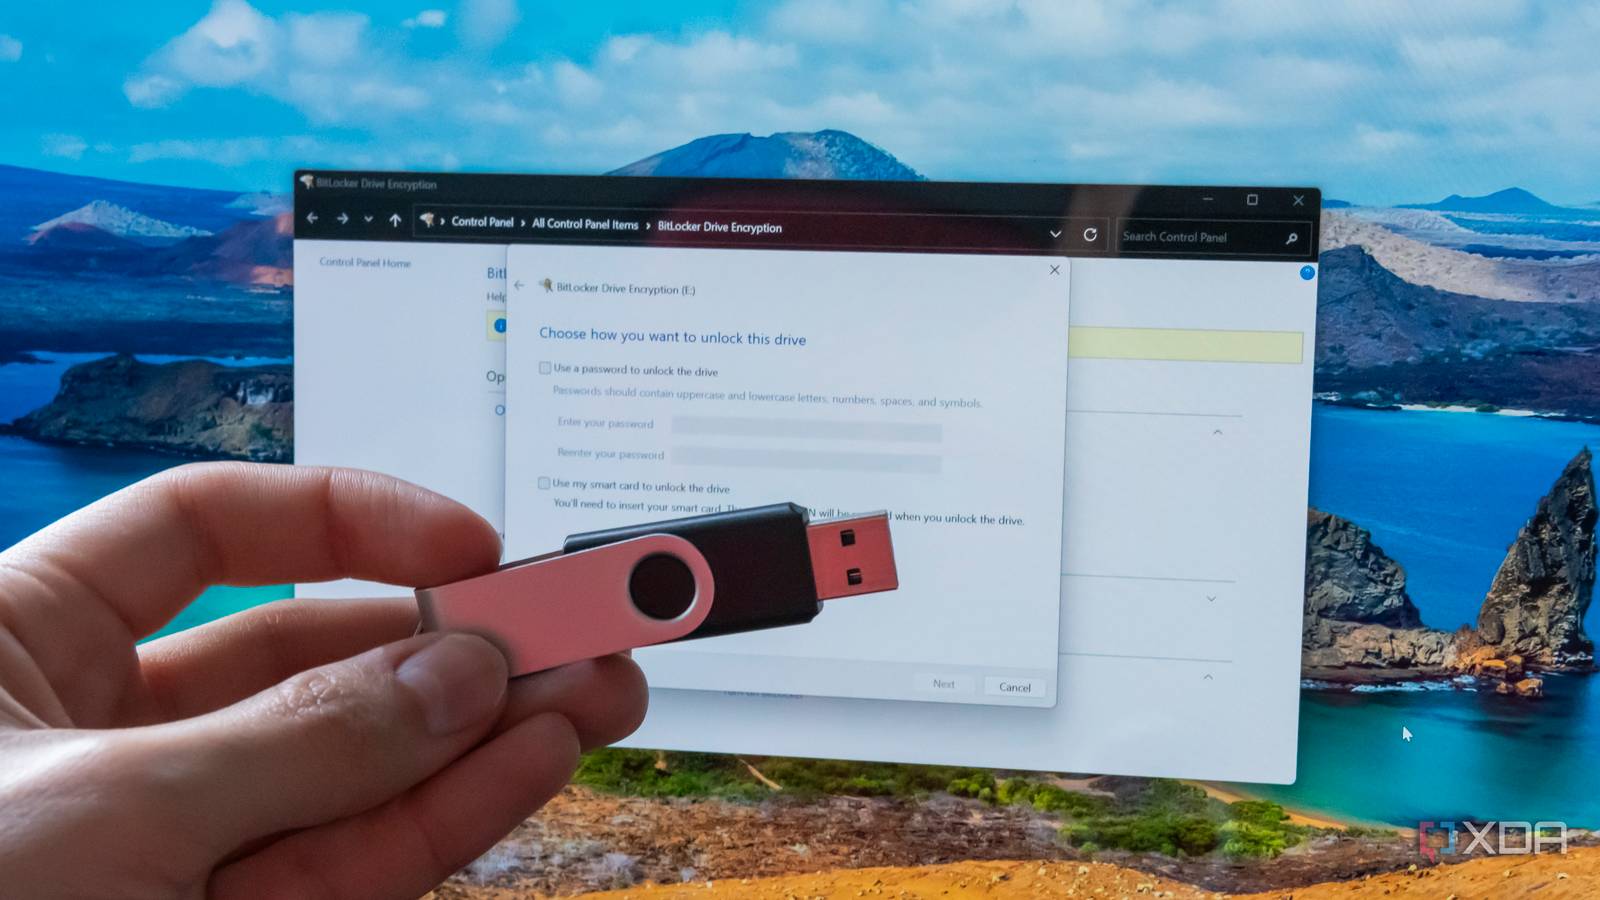
Key FactsUSB-Based Backdoor Breaches BitLocker Encryption
May 14, 2026 · Reading time: ~45 sec.
Summary created with AI assistance · Source: tomshardware.com
Summary created with AI assistance · Source: tomshardware.com
- The YellowKey zero-day exploit allows complete access to BitLocker-encrypted drives by copying files to a USB stick and rebooting into recovery mode.
- The exploit’s files vanish from the USB after use, suggesting a concealed backdoor that raises serious security and political concerns.
- YellowKey affects Windows Server 2022 and 2025 but not Windows 10, and it can bypass TPM-and-PIN configurations.
- Another exploit, GreenPlasma, enables local privilege escalation to system-level access, posing significant risks especially to server systems.
could have made some insane cash selling this, but no amount of money will stand between me and my determination against Microsoft.— Chaotic Eclipse (Nightmare-Eclipse) – regarding the YellowKey zero-day exploit and their stance against Microsoft.
A security researcher says Microsoft secretly built a backdoor into BitLocker, releases an exploit to prove it
techspot.com/news/112410-security-researcher-microsoft-secretly-built-backdoor-bitlocker-releases.html


Zero-day exploit completely defeats default Windows 11 BitLocker protections: It's not entirely clear how the exploit works. Microsoft says it's investigating.
arstechnica.com/security/2026/05/zero-day-exploit-completely-defeats-default-windows-11-bitlocker-protections/


Windows BitLocker zero-day gives access to protected drives, PoC released: A cybersecurity researcher has published proof-of-concept (PoC) exploits for two ...
bleepingcomputer.com/news/security/windows-bitlocker-zero-day-gives-access-to-protected-drives-poc-released/
After Bluehammer: Frustrated researcher leaks another Windows exploit - Golem.de: Attackers can use the exploit to gain system privileges on Windows systems due ...
golem.de/news/nach-bluehammer-frustrierter-forscher-leakt-weiteren-windows-exploit-2604-207637.html

BitLocker key required: April update locks out Windows users - Golem.de: Microsoft’s April Patch Day is giving admins more work than expected ...
golem.de/news/bitlocker-key-noetig-april-update-sperrt-windows-nutzer-aus-2604-207620.html

Trouble with Microsoft: Frustrated researcher leaks zero-day exploit for Windows - | Golem.de
golem.de/news/zoff-mit-microsoft-frustrierter-forscher-leakt-zero-day-exploit-fuer-windows-2604-207270.html

After May Patch Day: Bitlocker suddenly blocks Windows 10 users - | Golem.de: Some Windows 10 computers no longer boot due to the KB5058379 update ...
golem.de/news/nach-mai-patchday-bitlocker-sperrt-windows-10-nutzer-ploetzlich-aus-2505-196258.html

Next