
Microsoft asks IT admins to reach out for Windows IIS failures fix:
Microsoft has asked businesses to reach out for advice on how to temporarily mitigate a ...
bleepingcomputer.com/news/microsoft/microsoft-asks-it-admins-to-reach-out-for-windows-iis-failures-fix/
Photo: bleepingcomputer.com · view article
MSMQ Glitch Disrupts Enterprise Apps and IISDecember 2025 Windows updates caused MSMQ failures on enterprise devices, with temporary fixes offered via Microsoft Support.
Key FactsDec 17, 2025 · Reading time: ~30 sec.
Summary created with AI assistance · Source: bleepingcomputer.com
Summary created with AI assistance · Source: bleepingcomputer.com
- A known MSMQ issue affects Windows 10 22H2 and Windows Server 2016 and 2019 after recent security updates.
- This bug causes enterprise applications and IIS sites to fail with resource and misleading disk space errors.
- The problem arises from changed permissions requiring MSMQ users write access to a normally restricted system folder.
- Microsoft advises IT admins to contact business support for a workaround as a permanent fix is still pending.
Story Details
| Last Updated | |
| Total Articles | 1 |
Main Topics

Microsoft's web server software, included in most recent versions of Microsoft Windows

Similar to This
Previous

Detecting diseases through body odor? New laser technology shows potential for non-invasive diagnostics
medicalxpress.com/news/2026-09-diseases-body-odor-laser-technology.html


Computerworld Jul 17
CISA urges immediate SharePoint hardening as exploits mount: Three actively exploited SharePoint vulnerabilities have landed in the KEV catalog ...
computerworld.com/article/4197818/cisa-urges-immediate-sharepoint-hardening-as-exploits-mount-2.html


dlvr.it Jun 04
OpenAI's Codex chains decade-old DoS techniques into HTTP/2 Bomb: Codex drops an HTTP/2 Bomb
theregister.com/security/2026/06/04/openais-codex-chains-decade-old-dos-techniques-into-http/2-bomb/5251377
Computerworld Dec 20 25
Microsoft warns MSMQ may fail after update, breaking apps: A security update issued on December Patch Tuesday changes the MSMQ security model ...
computerworld.com/article/4108289/microsoft-warns-msmq-may-fail-after-update-breaking-apps.html


Windows Emergency Update Corrects Message Queuing Problems: Windows security updates are causing problems with Message Queuing (MSMQ) in Windows 10 and Server up ...
heise.de/news/Update-ausser-der-Reihe-Microsoft-fixt-Message-Queuing-Probleme-11120586.html

Computerworld Oct 21 25
Security patch or self-inflicted DDoS? Microsoft update knocks out key enterprise functions
computerworld.com/article/4075977/security-patch-or-self-inflicted-ddos-microsoft-update-knocks-out-key-enterprise-functions.html


Microsoft issues fix as Windows 11 25H2, 24H2 KB5066835, KB5065789 break many IIS websites - Neowin
neowin.net/news/microsoft-issues-fix-as-windows-11-25h2-24h2-kb5066835-kb5065789-break-many-iis-websites/
Microsoft employee confirms Windows 11 may never fix a key internet feature for office PCs
neowin.net/news/microsoft-employee-confirms-windows-11-may-never-fix-a-key-internet-feature-for-office-pcs/


If you deleted that mysterious Windows file Microsoft told you not to, there's a new script to restore it
tomshardware.com/software/windows/if-you-deleted-that-mysterious-windows-file-microsoft-told-you-not-to-theres-a-new-script-to-restore-it
Key FactsMicrosoft offers remedy for deleted inetpub folders
Jun 8, 2025 · Reading time: ~45 sec.
Summary created with AI assistance · Source: heise.de
Summary created with AI assistance · Source: heise.de
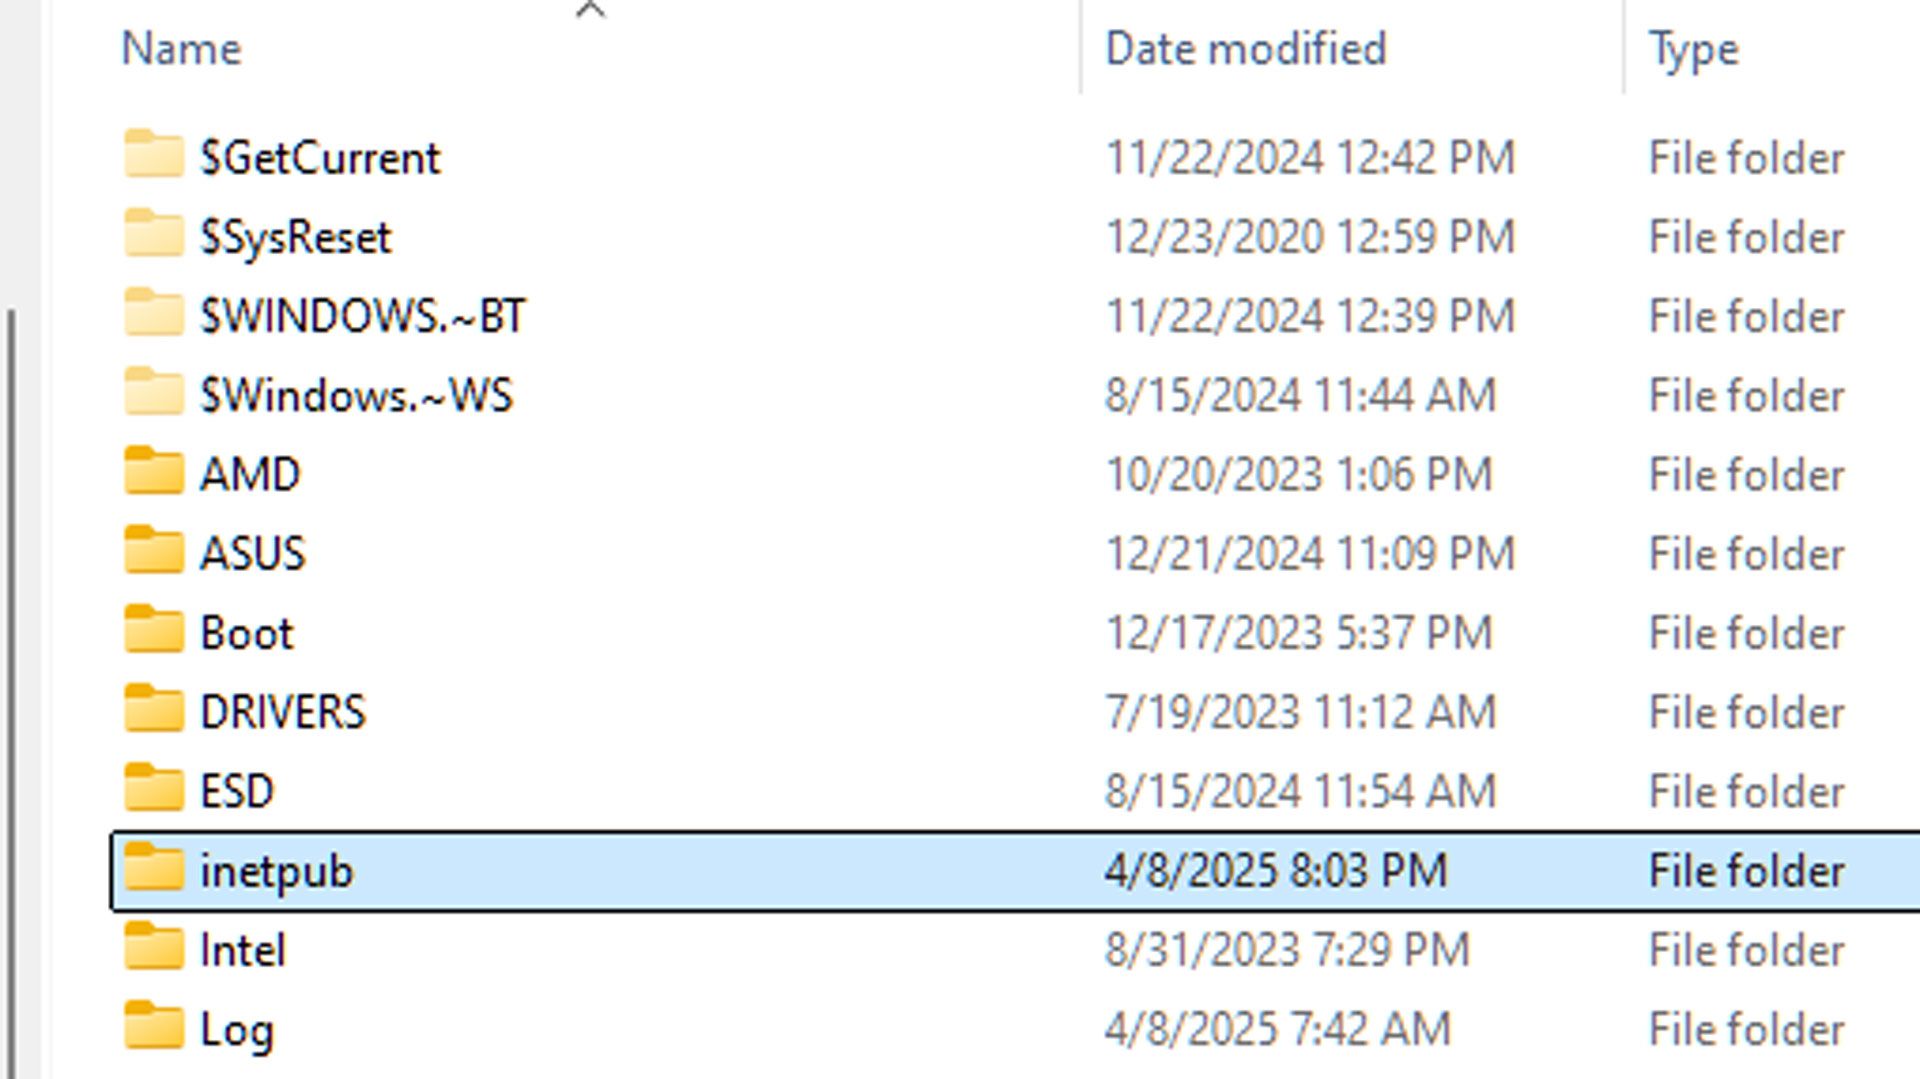
- Microsoft’s April security update KB5055528 created the “inetpub” folder on Windows systems.
- Microsoft says a deleted directory requires immediate remediation, while Kevin Beaumont reported that it can block later security updates.
- Set-InetpubFolderAcl recreates the folder, applies correct permissions, and requires administrator rights to run.
- On certain server versions, the script also updates ACLs for “DeviceHealthAttestation,” created by February 2025 security updates.
On systems where KB5055528 [the April security updates] are installed, but the '%systemroot%\\inetpub' directory has been deleted, immediate remediation is required. If the 'inetpub' directory has been deleted, you must run the remediation script Set-InetpubFolderAcl.ps1— Microsoft, in its updated security advisory addressing CVE-2025-21204 and the Set-InetpubFolderAcl.ps1 remediation script

Your Windows PC might be at risk if you deleted the "inetpub" folder, but there’s a fix
xda-developers.com/deleted-inetpub-folder-windows-fix/


Microsoft warns that anyone who deleted mysterious folder that appeared after latest Windows 11 update must take action to put it back
techradar.com/computing/windows/microsoft-warns-that-anyone-who-deleted-mysterious-folder-that-appeared-after-latest-windows-11-update-must-take-action-to-put-it-back
Key FactsMicrosoft's Update Creates Empty Folder for Security Reasons
Apr 16, 2025 · Reading time: ~30 sec.
Summary created with AI assistance · Source: techspot.com
Summary created with AI assistance · Source: techspot.com
- A recent Windows security update has created a new empty folder named 'inetpub' in the system root directory.
- This folder is linked to a security vulnerability patch and is associated with Microsoft's Internet Information Services.
- Microsoft has advised users not to delete the folder as it is part of security enhancements.
- It remains unclear how an empty folder contributes to mitigating security vulnerabilities.

Why is Windows 11's April update creating a mysterious 'inetpub' folder?: After installing April's KB5055523 update, Windows 11 users are spotting a new ...
pcworld.com/article/2684062/why-is-windows-11-latest-update-creating-a-mysterious-inetpub-folder.html

Windows Update drops empty 'intepub' folder in system, leaves users scratching heads after April update
tomshardware.com/software/windows/windows-update-drops-empty-intepub-folder-in-system-leaves-users-scratching-heads-after-april-update

Microsoft urges Exchange admins to remove some antivirus exclusions: Microsoft says some antivirus exclusions previously recommended for Exchange servers should ...
bleepingcomputer.com/news/security/microsoft-urges-exchange-admins-to-remove-some-antivirus-exclusions/

Researchers unearth Windows backdoor that’s unusually stealthy: Frebniis abuses Microsoft IIS to smuggle malicious commands in web traffic.
arstechnica.com/information-technology/2023/02/new-backdoor-targeting-windows-servers-is-ultra-stealthy/
dlvr.it Oct 31 22
Ordinary web access request or command to malware?: Cranefly group unleashes nasty little technique using Microsoft Internet Information Services (IIS) logs
theregister.com/2022/10/31/cranefly_microsoft_iis_symantec/
How to Find Your Vaccine History—and Store It Safely: Worries about polio, monkeypox, and Covid-19 are rising. Here’s how to gather your health information ...
wired.com/story/how-to-find-vaccine-history-store-it-safely/

Microsoft warns of stealthy backdoors used to target Exchange Servers: Microsoft is warning Outlook on the Web and Exchange Server customers to watch out for ...
zdnet.com/article/microsoft-warns-of-stealthy-backdoors-used-to-target-exchange-servers-email/

Microsoft Exchange servers worldwide hit by stealthy new backdoor: SessionManager scours memory for passwords, does recon, and installs new tools.
arstechnica.com/information-technology/2022/06/microsoft-exchange-servers-worldwide-hit-by-stealthy-new-backdoor/
Hackers steal Microsoft Exchange credentials using IIS module: Threat actors are installing a malicious IIS web server module named 'Owowa' ...
bleepingcomputer.com/news/security/hackers-steal-microsoft-exchange-credentials-using-iis-module/
Next